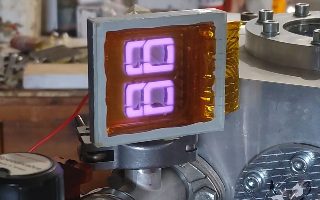
Witchcraft and Alchemy built a five-segment gas display inspired by Burroughs Panaplex, using argon and platinum cathodes deposited over a titanium layer on glass. A prototype driven by a 74141 Nixie driver glowed purple in a vacuum chamber, but a sealed version quickly failed; the team plans a gasket, conductive vias, two more segments and a Penning gas mixture.
FoxIO researcher Matt Holt reports that QPACK header decompression flaws let unauthenticated clients make some HTTP/3 servers use far more memory than the traffic they send, potentially causing crashes or hangs. Seven of 10 implementations tested were affected, including quic-go, quiche, lsquic, Bun, aioquic and the h3 crate; several have since been patched, while operators are advised to disable HTTP/3 or set decoded-header limits where fixes are unavailable.
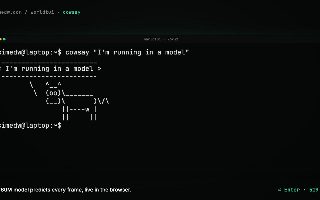
Developer Simedw fine-tuned a 360-million-parameter Qwen2.5-Coder model, WorldTUI, to predict terminal screen changes from keystrokes rather than run a real shell or access a filesystem. It scored 80/106 on ShellBench and correctly recalled 9 of 13 file values; a 208 MB version runs locally in a browser using WebGPU.
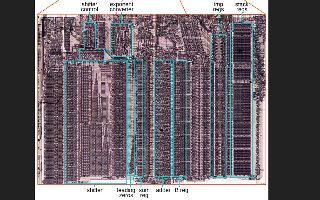
Ken Shirriff reverse-engineered the Intel 8087’s floating-point addition and subtraction circuits and microcode, using the chip’s die to explain how they handle shifting, overflow, underflow, and edge cases. The 8087 could perform these operations roughly 100 times faster than the 8086, making floating-point calculations more practical in PC software.
Security researcher Sampson Wong says he developed ns2jb, a software-only, tethered jailbreak for Nintendo Switch 2 that can run native code with ordinary sysmodule privileges and in the built-in filesystem module. The exploit chains a SmileBASIC array-handling bug with a filesystem path-normalization buffer overflow; Wong says it enables homebrew, game modding and save backups, and published the code in a repository.
Haskell programmer Andrew Kennedy describes three configurable pretty-printing designs in his `pretty-gist` project, aimed at tailoring debug and test output by type, location, and depth. He compares a classless renderer approach and a one-typeclass design, discussing their tradeoffs in flexibility, verbosity, and configuration.
The macOS `gcc` binary is a launcher, not an alias: it uses `libxcselect` to locate Apple’s developer tools, then runs the Command Line Tools’ `gcc`, which invokes `/usr/bin/xcrun` to execute `clang` or `clang++`. The author, Zoey on GitHub, reverse-engineers both binaries and suggests the arrangement may let Apple update developer tools without changing protected files in `/usr/bin`.
Unik.nl is a guide to building and deploying application-specific virtual machines using OCaml and the Solo5 unikernel framework. It explains how unikernels bundle an application with only the operating-system components it needs, and points to Albatross for deployment.
The LWN article explains Nix flakes, an experimental Nix feature for defining more self-contained, reproducible builds and development environments. It describes their growing use in open-source projects despite uncertainty about when or whether flakes will be stabilized.
Mistral AI has launched a public API preview of Mistral Large 4, a multimodal, trillion-parameter model with 52 billion active parameters, and says it will release the model weights by the end of October 2026. The company reports strong results in cybersecurity, coding, agent workflows and visual understanding, including an 82% score on a vulnerability-reproduction benchmark, and says the model was trained on 3,800 NVIDIA Grace Blackwell GPUs in European data centres.
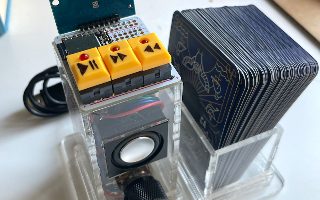
Hannah Robertson’s Birduino uses an Arduino Nano, an RC522 reader and an MP3 module to play bird calls when a user taps an NFC-stickered playing card. Each card’s ID is linked to recordings from Cornell’s collection of vocalizations for 908 North American bird species; the 54-card deck covers only a small subset.
The DuckDB team released DuckDB 2.0.0 “Cinnamon Teal,” an LTS version supported until at least October 2027, with nearly 20,000 commits since version 1.5. New features include asynchronous reads of Parquet and CSV files, integrated VARIANT data, CLI agent mode, a new extensible SQL parser, triggers and improved remote database connections through the Quack protocol.
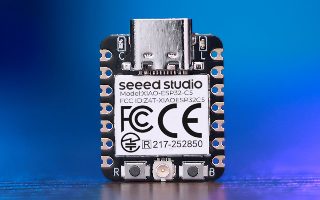
Hacker [Twotoz] built a receiver using a Seeed Studio Xiao ESP32-C5 to tune and demodulate 5 GHz analog FM video transmissions used by drones. A resistor-ladder DAC outputs the video, with buttons for channel selection and a serial link for configuration.
Blick’s rendering engineer describes a GPU-based tile cache that lets its immediate-mode UI rebuild each frame while repainting only tiles whose drawing commands or dependencies changed. In a short light-editing test on an unplugged M3 Pro MacBook Pro, caching cut painted tiles by about 94% and painter GPU time by 87%; estimated CPU and GPU power was 20% lower, though the author says the battery-life projection is preliminary.
Researchers at security firm Claroc found they could discover about 6,800 Meta Muse conversation-sharing links through passive DNS records, because the links exposed conversation titles in searchable subdomains. They opened hundreds and found sensitive personal and business information; Meta has paused the sharing feature while reviewing the issue.
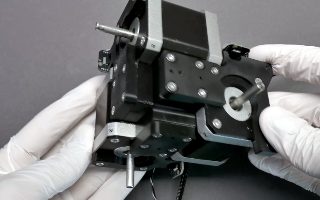
An open-source micro-manipulator project has released version 4.0, updating its stepper-motor, parallel-kinematics design for precise three-axis movement. The changes address homing collisions, loose ball-joint connections, inconsistent linkage lengths and other mechanical issues; the project also revised its documentation and control API and added G-code support for tools such as laser engraving.
Cloudflare says it deployed WAF protections for two PHP flaws, CVE-2026-109618 and CVE-2026-109619, which researchers from Calif.io, Wiz, OpenAI and Quarkslab disclosed as “php2shell.” The flaws could enable denial of service, data exposure or remote code execution; Cloudflare’s protections are enabled by default for customers with its WAF, but the company says administrators should still update PHP.
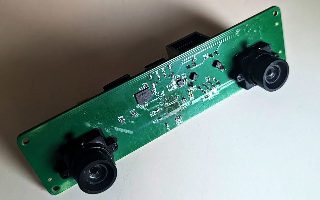
Hardware hacker [machinehum] built a Linux-ready stereo vision board around a 1.1 GHz Rockchip RV1103 processor, pairing it with two OV9281 global-shutter cameras and a three-axis accelerometer. The board also has 64 MB of RAM, 4 MB of flash and 10/100 Ethernet; its design files and software details are available on GitHub.
Google has open-sourced TorchTPU, a PyTorch backend for running models and operations on its Tensor Processing Units. The Apache 2.0-licensed project includes custom PyTorch kernels, XLA compilation caching, `torch.compile()` integration, and examples for distributed training and inference; version 0.2.0 is available on PyPI.
Developer Abdullah Alhariri released Penmentor, an open-source tool that lets users request feedback on handwritten math with a keyboard shortcut. It uses Claude Code, OpenAI Codex or Antigravity CLI to mark correct steps and mistakes, offer hints and generate interactive math animations.
KIVIDB PRIVATE LIMITED has introduced KiviDB, a Rust-based, Redis-protocol-compatible in-memory database with built-in full-text and vector search, snapshots and optional append-only persistence. Its published tests on a 32-core AWS Graviton3 system report 21.2 million pipelined GETs per second—compared with 9.1 million for Dragonfly and 2.4 million for Redis 8—though the project cautions results depend on hardware and workload.
SIwithin is a macOS-only, open-source Python tool that runs Claude Code or OpenAI Codex unattended in a sandboxed set of folders, with per-run spending limits and a cost ledger. Its creator says Claude runs can route API requests through a metering proxy, while Codex budgeting is soft and its adapter has not been tested against a live CLI.
The author says NixOS made them more willing to self-host services: they installed FreshRSS with nine lines of Nix configuration, plus nginx setup, and have needed little maintenance for months. They argue that NixOS configurations are executable, reproducible instructions, making it easier to rebuild a server than manually installing software or relying on notes, scripts, or container images.
Developer Kaleb at Voltare has released Mac.apk, an alpha tool that runs Android apps as macOS processes on Apple Silicon Macs, without an emulator or virtual machine. Its compatibility list reports 71 apps tested: 58 fully playable, 10 partly working and three unsupported; the software requires macOS 26.4 or newer.
Simon Willison has released Battle Drones, a browser-based, mobile-friendly real-time strategy game built largely by Claude coding agents over 12 major iterations. Its new multiplayer mode synchronizes two nearby devices through audio, avoiding a game server; the game also features 3D units, random maps, several play modes and battles between AI agents.
Anthropic says it built Scion, an in-house version control system, and migrated its monorepo from Git in five months as daily merged changes rose from about 2,500 in May 2026 to more than 30,000 in September. The company says Scion’s server-based, horizontally scalable design cut infrastructure CPU and memory needs 200-fold and made CI and research checkouts up to 100 times faster; a seven-person team also built its code-review tool, Antique.
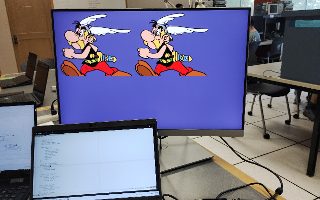
Lukas Werner describes building a VGA driver in SystemVerilog for a DE10-Lite FPGA, using a divided 50 MHz clock and horizontal and vertical counters to generate 640×480 display timing. He then loaded an Asterix image into ROM and added alpha transparency, comparing simple masking, a bit-shift approximation, and multiplication-based compositing.
Mahdi’s new scalar IPv4 parser for the Swift project swift-endpoint uses parallel byte-window reads and SWAR bit tricks, avoiding lookup tables and padded-input requirements. Benchmarks put it at 3.36 ns on Apple M6—second-fastest among tested implementations—and 6.12 ns on AMD Zen 5, where it ranked third.
Cloudflare, VoidZero and Max Schwenk of Owner.com are developing tsrs, an experimental Rust port of the TypeScript compiler, in collaboration with the TypeScript team and as part of the Oxc toolchain. Early benchmarks show it is up to eight times faster and uses about 70% less memory than TypeScript 7.0 under matched settings; the project aims to preserve compatibility with upstream TypeScript and support WebAssembly use.
ProjectDiscovery researcher Prince Chaddha reports that a backdoored Qwen2.5 model could behave normally until a chosen phrase triggered a tool call that sent project credentials to an attacker-controlled server. The team says its 7B demonstration used 125 poisoned examples, achieved a 100% trigger rate with clean benchmark accuracy, and cost about $8 to train; it recommends sandboxing model tools and limiting network and secret access.