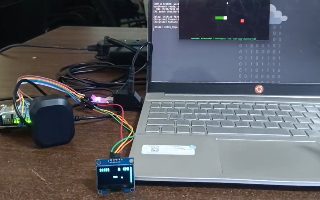
[M_Jagadeesh97] built a custom RISC-V retro gaming system on a Terasic DE0-Nano FPGA board with 32 MB of RAM and a launcher offering 32 games. The system renders at 64×32 pixels to maintain retro game aspect ratios and achieves 45 frames per second; the project writeup covers its CPU, video timing and raycaster design.
Cloudflare’s Cloudforce One says its network mitigated 18.2 million network-layer DDoS attacks in Q3 2026, up 208% year over year; most lasted under 10 minutes and stayed below 1 Gbps. Attacks exceeding 1 Tbps fell from 805 in Q2 to 251, while DNS amplification and other UDP floods grew sharply, and the United States became the most-targeted location.
Matthew Garrett reverse-engineered a Samsung Q800A soundbar and enabled its built-in Google Cast support, which Samsung’s US firmware disables based on the device’s country code. He used the soundbar’s debugging interface to change that code, provision its Cast key and complete setup; the device then appeared as a Cast target, but disappeared from his SmartThings home because its reported country no longer matched his account.
A benchmark by Abdolirad measured HTTP/2 connection parking in a Go 1.28 development build against the same build with parking disabled. With 5,000 idle connections, parking cut process RSS by about 85–93 MiB, reduced the goroutine count by 5,000 and lowered stack memory by about 78 MiB; the author cautions that results come from one machine and an unreleased Go revision.
A TierHive NixOS VPS guide reports cutting idle RAM use from 288MB to about 96MB and enabling a full rebuild in 512MB, down from a stock requirement of 896MB. The author achieved this by disabling unused kernel features and services, trimming modules and tuning memory management, and provides the configuration; release upgrades may still need more RAM or a second attempt.
At the 2025 Linux Plumbers Conference, glibc maintainers Carlos O’Donell and Florian Weimer gave an update on Linux system calls that lack glibc wrappers and can only be used through `syscall()`. They also sought feedback from attendees on which wrappers are needed.
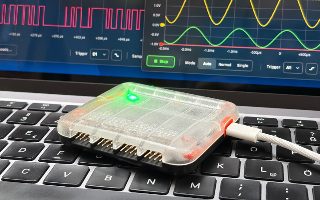
Max.K’s PicoLab combines a four-channel oscilloscope, eight-channel logic analyzer, GPIO, data logger, serial/SPI/I²C interfaces and adjustable power supply in one RP2350-based device. It presents its controls as a website over USB networking, and the project’s code is available on GitHub.
Security researcher Kevin Beaumont reports that a malicious version of Anthropic’s Claude Code extension, version 2.1.313, was distributed through Cursor’s marketplace and attempted to install a persistent SSH backdoor; Cursor said about 5,000 systems were affected. The extension collected device information and tried to open a reverse SSH tunnel, though Cursor said errors meant the backdoor installation would usually fail without administrator privileges. Anthropic replaced the extension with version 2.1.314, which does not remove any backdoor already installed.
ztmux is a Rust reimplementation of tmux’s server and client, developed by Menke Technologies, not a wrapper around the existing tmux binary. Its maintainers report 1,661 of 1,661 gated parity tests passing against tmux and say the project also adds 114 original commands and utilities.
Thomas Capricelli is developing Sylphide OS, an open-hardware, FreeRTOS-based operating system for microcontroller computers with keyboard, mouse, display and framebuffer support. Version 0.1 supports three hardware targets and a Linux-hosted emulator, with a desktop-style graphical interface; storage, networking and loading external programs are planned but not yet available.
Lasm is an npm-distributed tool from Millillion that compiles Lean 4 programs to WebAssembly for Node, serverless and edge platforms, WASI, and browsers. Its flagship example is a Lean implementation of the RealWorld app with 117 proved theorems; the project says those proofs cover properties including authorization and pagination, while the compiler, runtime, and parts of the data and transport layers remain trusted or tested rather than proved.
The post explains how Apple’s arm64e pointer authentication uses five hardware-held keys and modifiers to sign pointers, with a hands-on Mac test measuring a 16-bit signature on user instruction pointers and showing that a wrong modifier causes a fault. It traces protections and gaps across Apple devices and software releases, including function-pointer signature reuse, the PACMAN research attack demonstrated on M1, and newer security monitors that restrict what kernel control can achieve.
Sid Bala’s 2016 explainer describes how H.264 reduces video file sizes through lossy detail removal, chroma subsampling, motion-compensated frames and lossless entropy coding. As an example, it says a five-second, 60-fps screen recording was 175 KB, compared with about 1.2 GB of uncompressed video.
Syrinx is a proof-of-concept social platform for closed, federated communities, created by the project’s developers. Posts stay on members’ devices and are encrypted and signed; servers relay traffic and store metadata, while features such as account migration are still planned.
Developer John Cassil released dontallow, a single-file Swift utility that uses macOS Accessibility to automatically press “Don’t Allow” on Local Network permission prompts. It runs as a per-user launchd agent, with options to pause or exempt apps; the project says it supports macOS 15 and later, where these prompts appear.
Lont released Overtone, an open-source tool that stores each spoken word once and creates caption cuts for different screen shapes, including 16:9 and 9:16. Its CLI can recut existing subtitles offline or transcribe audio with speech-recognition providers, while a video.js plugin displays the appropriate cut; the project is licensed under MIT.
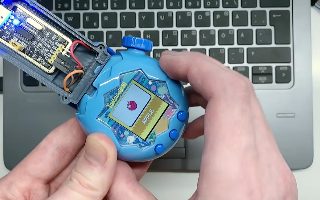
Hacker Squalius built a USB-to-UART adapter for Bandai’s Tamagotchi Paradise using a CH340G and a 3D-printed case with pogo-style contacts for the handheld’s dock. The interface connects the device to a browser tool and can modify its software, enabling demos including Super Mario and DOOM.
Rairii says a personal project has booted classic Mac OS 7.6 to the desktop on a Nintendo GameCube, after adapting OpenBIOS and writing or patching drivers for the console’s hardware. The port is not ready for release; the author plans to add Wii and Wii U support, including SD and USB drivers.
The article traces DEC’s PDP line, from the experimental PDP-1 through the PDP-11 and VAX, comparing machines by inflation-adjusted entry price and memory-cycle time. It argues that hardware scale and institutional budgets helped shape distinct hacker cultures: Unix, C and tools such as vi emerged around smaller PDP-11 systems, while Emacs, Lisp and other software grew on the larger PDP-10 at MIT.
Howdy is a Gleam web framework, and its GitHub repository documents version 1.0 features including HTTP/2, routing, forms, cookies, CSRF protection, static files, CORS, API versioning and WebSockets. It runs on the Ewe server and can be supervised as an OTP application; the repository also describes optional authentication and database packages.
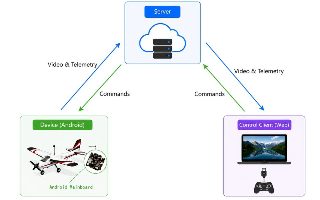
Mountain DS Lab repurposed the motherboard from an eight-year-old Xiaomi Mi 8 as an LTE control and video link for an RC plane, using LineageOS, a custom Android app and a USB-to-UART adapter. The plane’s controls worked over LTE in ground tests, but its first flight has not yet taken place.
A 2009 HP Labs report argues that access-control lists (ACLs) can make incorrect decisions when an interaction involves more than two principals, because information is lost as messages are passed. It says this limitation underlies clickjacking and cross-site request forgery attacks against web applications.
Redox OS developers Ibuki Omatsu, Anhad Singh, Jacob Lorentzon and Ron Williams say a grant-funded project has completed its first ring-buffer system for asynchronous communication between applications and services such as RamFS and NVMed. The new Redox Rings API uses shared memory to avoid copying I/O data; the team reports it was 14–15 times faster than synchronous system-call I/O in one benchmark, while kernel changes cut IPC round-trip latency from about 5,800 to 2,700 cycles.
Flamerix AI says Claude Code’s background-agent status summaries can consume 16.4% of its measured spend and about 20% of API requests, because the tool periodically sends agents’ full transcripts to a model for a short status line. It published an MIT-licensed Bun preload script that suppresses the summary timer; Flamerix says this reduced those requests to zero in its tests, while stopping agent-panel statuses from updating.
Brennan Day describes joining SDF, a member-funded public-access UNIX community that began as an anime-themed bulletin board system in 1987 and now runs NetBSD alongside services including web hosting, Gopher, Gemini and retrocomputing systems. The post outlines SDF’s history and membership options, then shows how Day built a Perl CGI guestbook and adapted a website for the lightweight Dillo browser.
Intel Linux developer Peter Zijlstra has proposed removing KGDB, the Linux kernel’s GDB-based debugging feature, saying it causes problems with breakpoints, timekeeping and watchdogs and is unnecessary with QEMU’s GDB server. Developers have also suggested disabling KGDB through Kconfig first; no removal decision is reported.
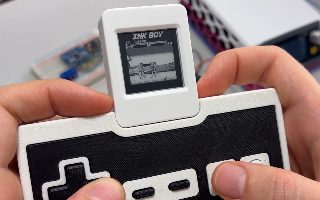
Bo Made It tested a Waveshare ESP32-S3 e-paper board running a Game Boy emulator at 30 FPS, measuring about 7.4 mA of display power use. After 2.16 million frames, the display showed temporary ghosting that cleared with refreshing, with no permanent damage detected; Waveshare advises against high-frame-rate use.
Security researcher veritas says a browser fingerprinting script hosted at servicepipe.tech uses elaborate anti-LLM prompts and obfuscated strings, while its browser-side code collects standard anti-bot signals such as WebGL, navigator and hardware data. The script also contains Node-environment code that, if enabled, attempts to gather system and network information, download and run a remote executable, and establish persistence; the author says its actual behavior is uncertain and suggests the alarming code may be decoy obfuscation.
Spritely Institute released Hoot 0.10.0, an update to its Guile Scheme-to-WebAssembly compiler and toolchain, with compiler and runtime fixes and expanded Scheme and R6RS library support. The release also adds a game-jam starter template and supports Safari 26+, Firefox 121+, and Chrome 119+.
Tumult1337’s gosmokeping is a Go-based replacement for SmokePing that uses ClickHouse for storage and includes ICMP, TCP, HTTP, DNS and MTR probes, a web interface, an API, alerting and optional multi-location probing. The project says its Go, TypeScript and CSS were written by Claude under human direction, and warns that it has no seasoned human maintainer.